 Schildmark
Platform
Every alert, in one list you can trust
Endpoints, network sensors, firewalls, Microsoft 365 and your cloud accounts report into one console. Severity is normalised across all of them, so a critical alert means the same thing whatever raised it.
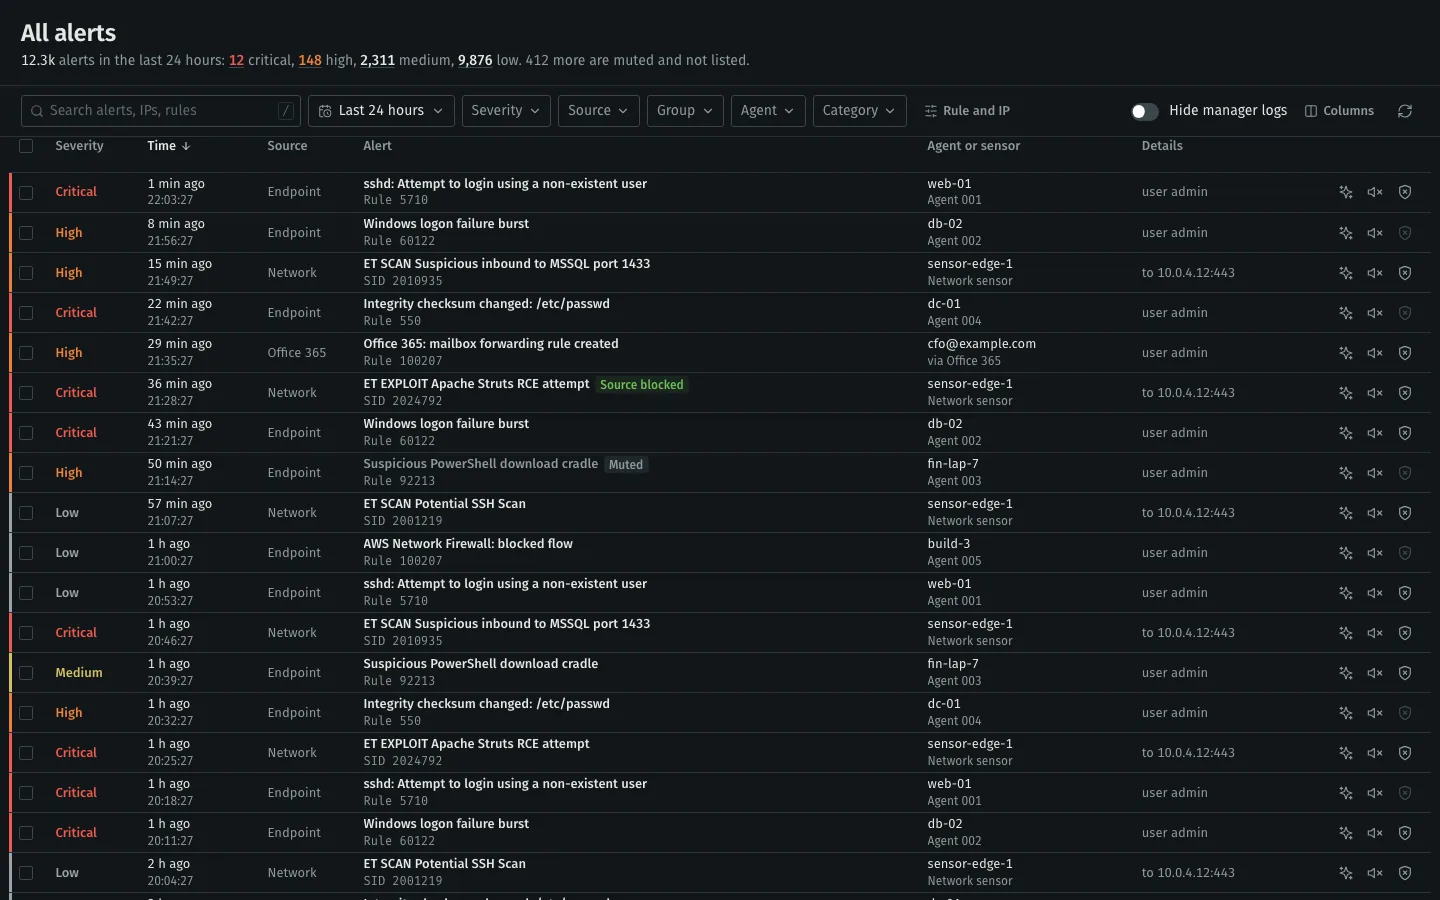
- One sentence first. How many alerts came in, by severity, and how many are muted and left out.
- Where it came from. Endpoint, network sensor or a connected service, side by side in the same list.
- What already happened. A blocked source or a mute shows on the row, so nobody acts twice.
- Act on the row. Ask the analyst, mute the rule, or block the source address.
What it reads
Everything below is set up by an administrator in the console. Nothing needs access to the server. All integrations
| Source | What arrives | How |
|---|---|---|
| Endpoints | Logs, file integrity, configuration checks (CIS), software inventory, vulnerable packages | The monitoring agent on Windows, macOS and Linux |
| Network | Intrusion detection alerts | A Suricata sensor on your network |
| Firewalls and switches | Device logs, read by the detection rules | Syslog on UDP 514, from devices you list |
| Microsoft 365 | Sign-ins, Exchange, SharePoint and DLP events | Office 365 Management API |
| AWS | CloudTrail, GuardDuty, WAF, Inspector, Network Firewall | A read-only role you create |
| Google Cloud | Cloud Audit Logs, Security Command Center findings | Pub/Sub |
| Security tools | Microsoft Defender for Endpoint, Microsoft Intune, Sophos Central, Cloudflare | Connectors that poll every 30 minutes |
| Your internet edge | Findings of the external scanner | Scheduled scans of hosts you are authorised to scan |
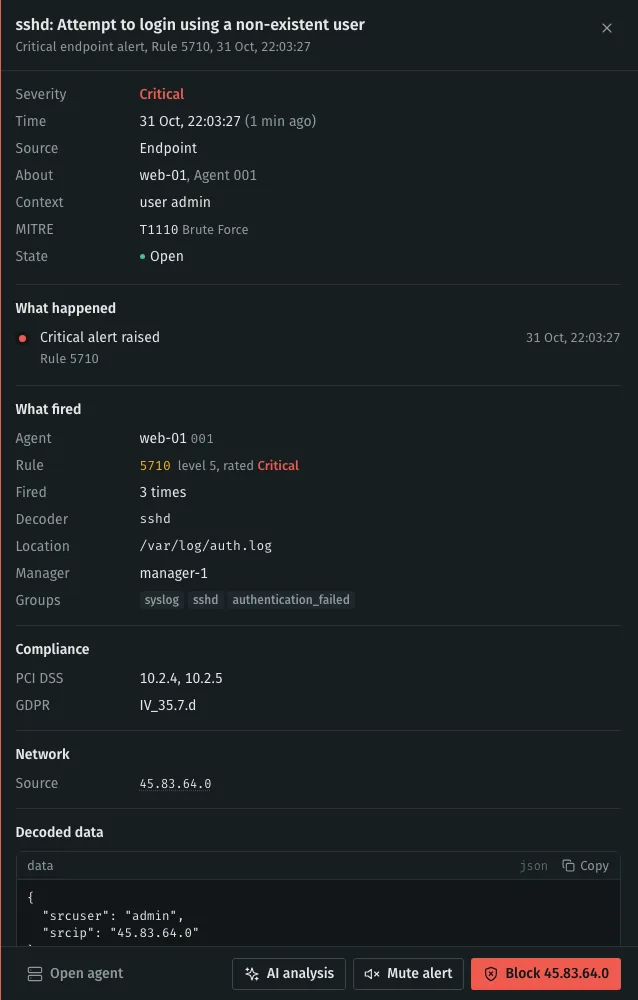
Open an alert and everything about it is there
- What fired
- The rule, its level, how many times it fired, and the decoded log line.
- MITRE ATT&CK
- The technique the rule maps to, for example T1110 Brute Force.
- Compliance
- The controls this alert is evidence for, which the compliance page counts.
- Mute
- Needs a rule or signature, a classification (false positive, known benign, tuning) and a reason. Mutes are pushed to the sensors, not only hidden in the console.
- Block
- Sends the source address to the blocking points you have connected.
Vulnerabilities, checked before they are shown
The agents report vulnerable packages. Before a finding is shown, it is corroborated against vendor and NVD data every 30 minutes and marked confirmed, needs review or not applicable. Only confirmed findings count as open.
- Exploited first
- Investigation puts findings on CISA’s Known Exploited Vulnerabilities list at the top, then the ones that came back after a fix.
- Fixes tracked
- A finding that disappears is checked against the fixed version; a kernel fix waits until the machine has restarted.
- Reopened
- A finding that returns within 30 days is reopened, not counted twice.
See who is attacking what
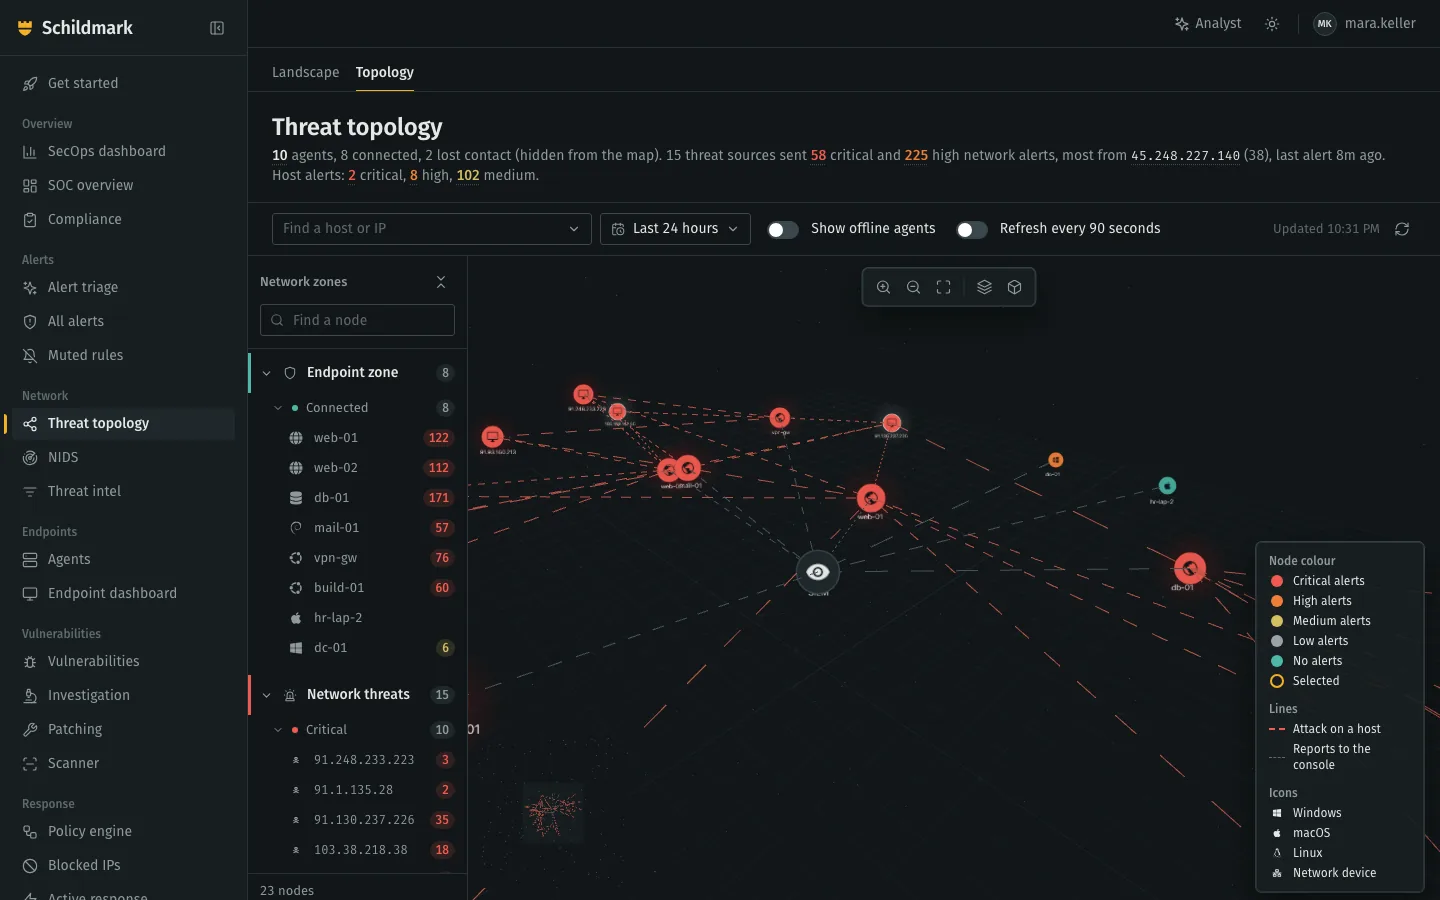
Threat topology draws your machines, the addresses attacking them and the alerts between them, coloured by the worst alert. Addresses are enriched with reputation from AbuseIPDB, VirusTotal, AlienVault OTX or your own MISP.
Talk to sales
Tell us about your machines, your firewalls and the audit you are preparing for. We answer within one working day.